



TL;DR: Candidate fraud is a cross-functional risk. TA owns process and candidate flow. Security owns identity and technical risk. Legal owns compliance and documentation. Hiring managers own in-interview judgment. A RACI matrix turns these informal assumptions into a defensible operating model. BrightHire embeds hiring fraud detection into the interview workflow, surfacing deepfake and identity risk signals and pushing an auditable record into your ATS.
Candidate fraud doesn’t stay in TA’s lane. It touches Security, Legal, HR, and hiring managers, and when it surfaces, most teams improvise the response. That improvisation is where the real exposure lives.
Most fraud discussions focus on detection. But an equally important question is “who owns the response when we do detect it?” Candidate fraud spans identity, credentials, resume claims, and AI-manipulated video, and no single function can own all of it. When your team detects fraud, you need a response that’s already defined, not one improvised in a Slack thread between four departments.
This article maps candidate fraud ownership across TA, Security, Legal, and hiring managers, then gives you a RACI framework you can adapt to your org. TA leaders coordinate the response across functions and ensure each part of the risk has a clear owner.
What constitutes fraud in modern hiring?
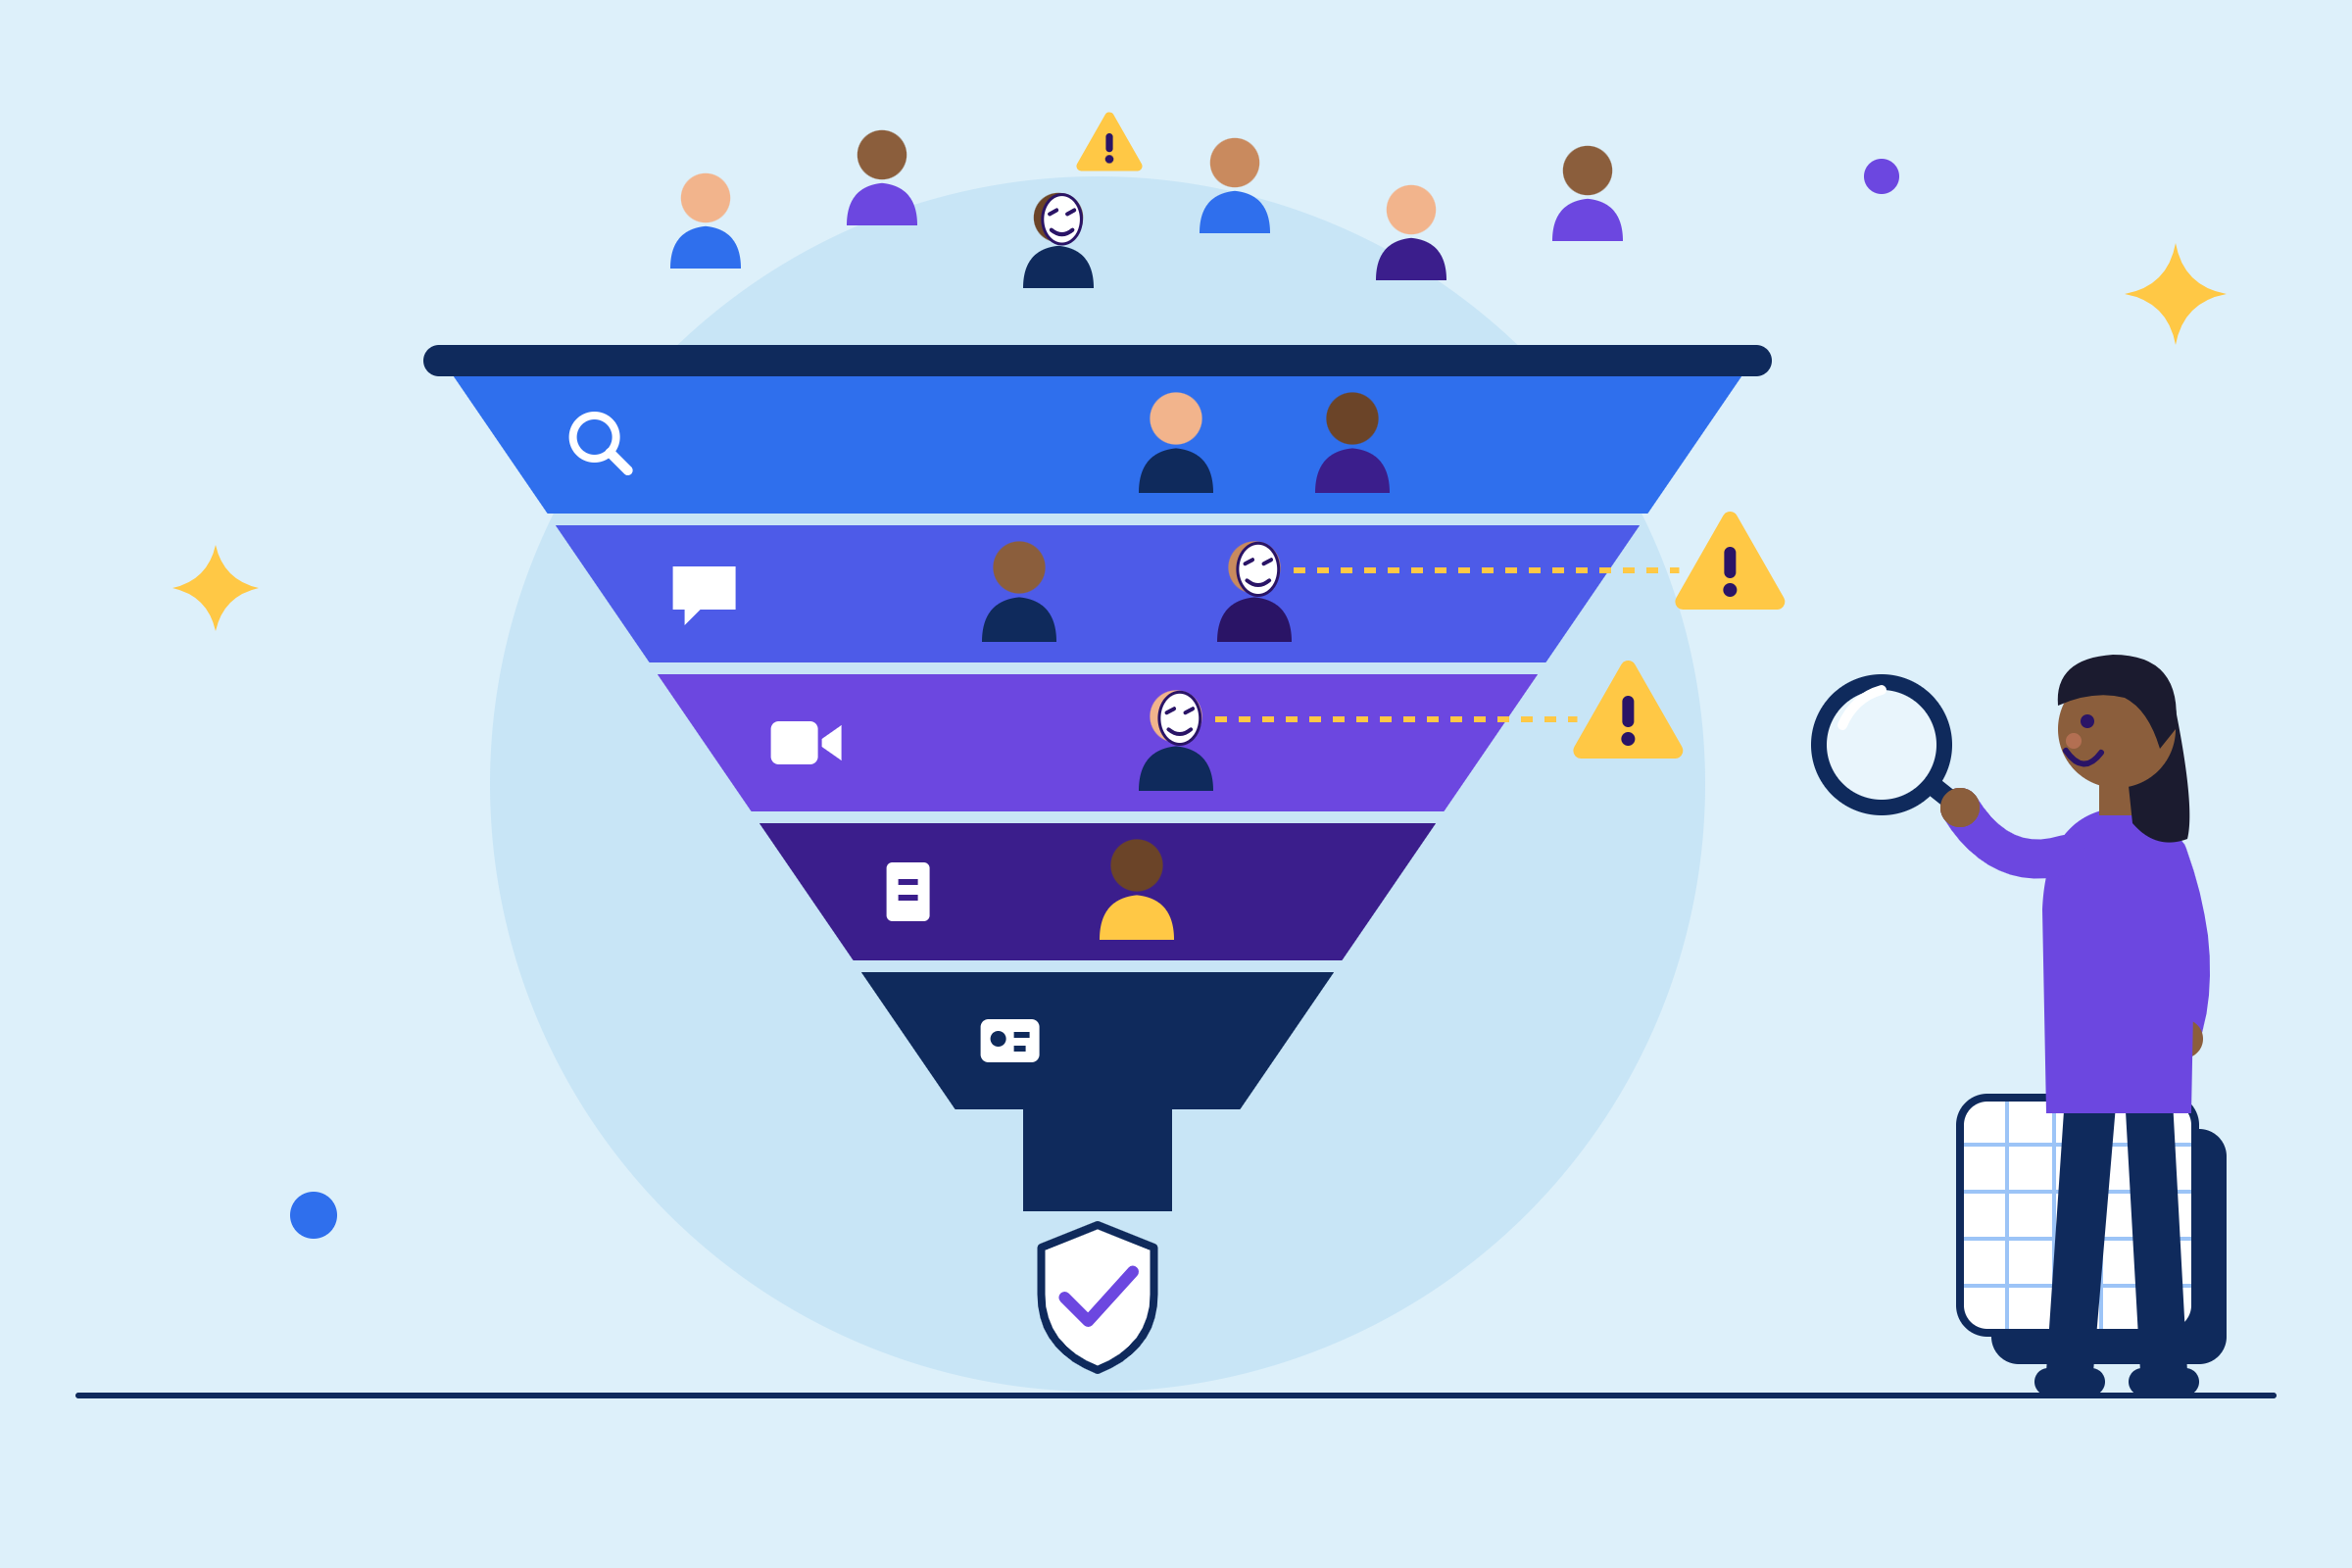
Candidate fraud enters the hiring pipeline at multiple stages, and each type requires a different detection approach and a different owner. Gartner predicts that by 2028, one in four candidate profiles worldwide will be fake. This is a trajectory that makes formal ownership models a near-term operational necessity, not a future-state consideration.
Understanding where each fraud type enters your process is the first step toward assigning ownership, which is why we at BrightHire built our candidate fraud resource hub around the full hiring funnel rather than a single checkpoint.
Detect resume fraud patterns
Resume fraud covers inflated titles, fabricated employment dates, fake degrees, and invented skills. It’s often the first signal a hiring team encounters, but it’s not the only one. Recruiters are the first line of detection during screening and intake, when they review applications and conduct initial conversations.
Recognize imposter candidate risk
An imposter candidate is someone other than the applicant who completes the interview. The operational risk is direct: the person you hire isn’t the person you evaluated, and imposter risk is highest in remote, async, and high-volume hiring where face-to-face verification is limited. Checkr’s 2025 Hiring Hoax Survey found that 31% of managers interviewed a fake candidate, so this isn’t a fringe risk. Industry analysis frames interview fraud, including proxy candidates and deepfakes, as one of three primary fraud categories CHROs now track alongside credential misrepresentation and identity fraud.
Spot AI deepfakes in interviews
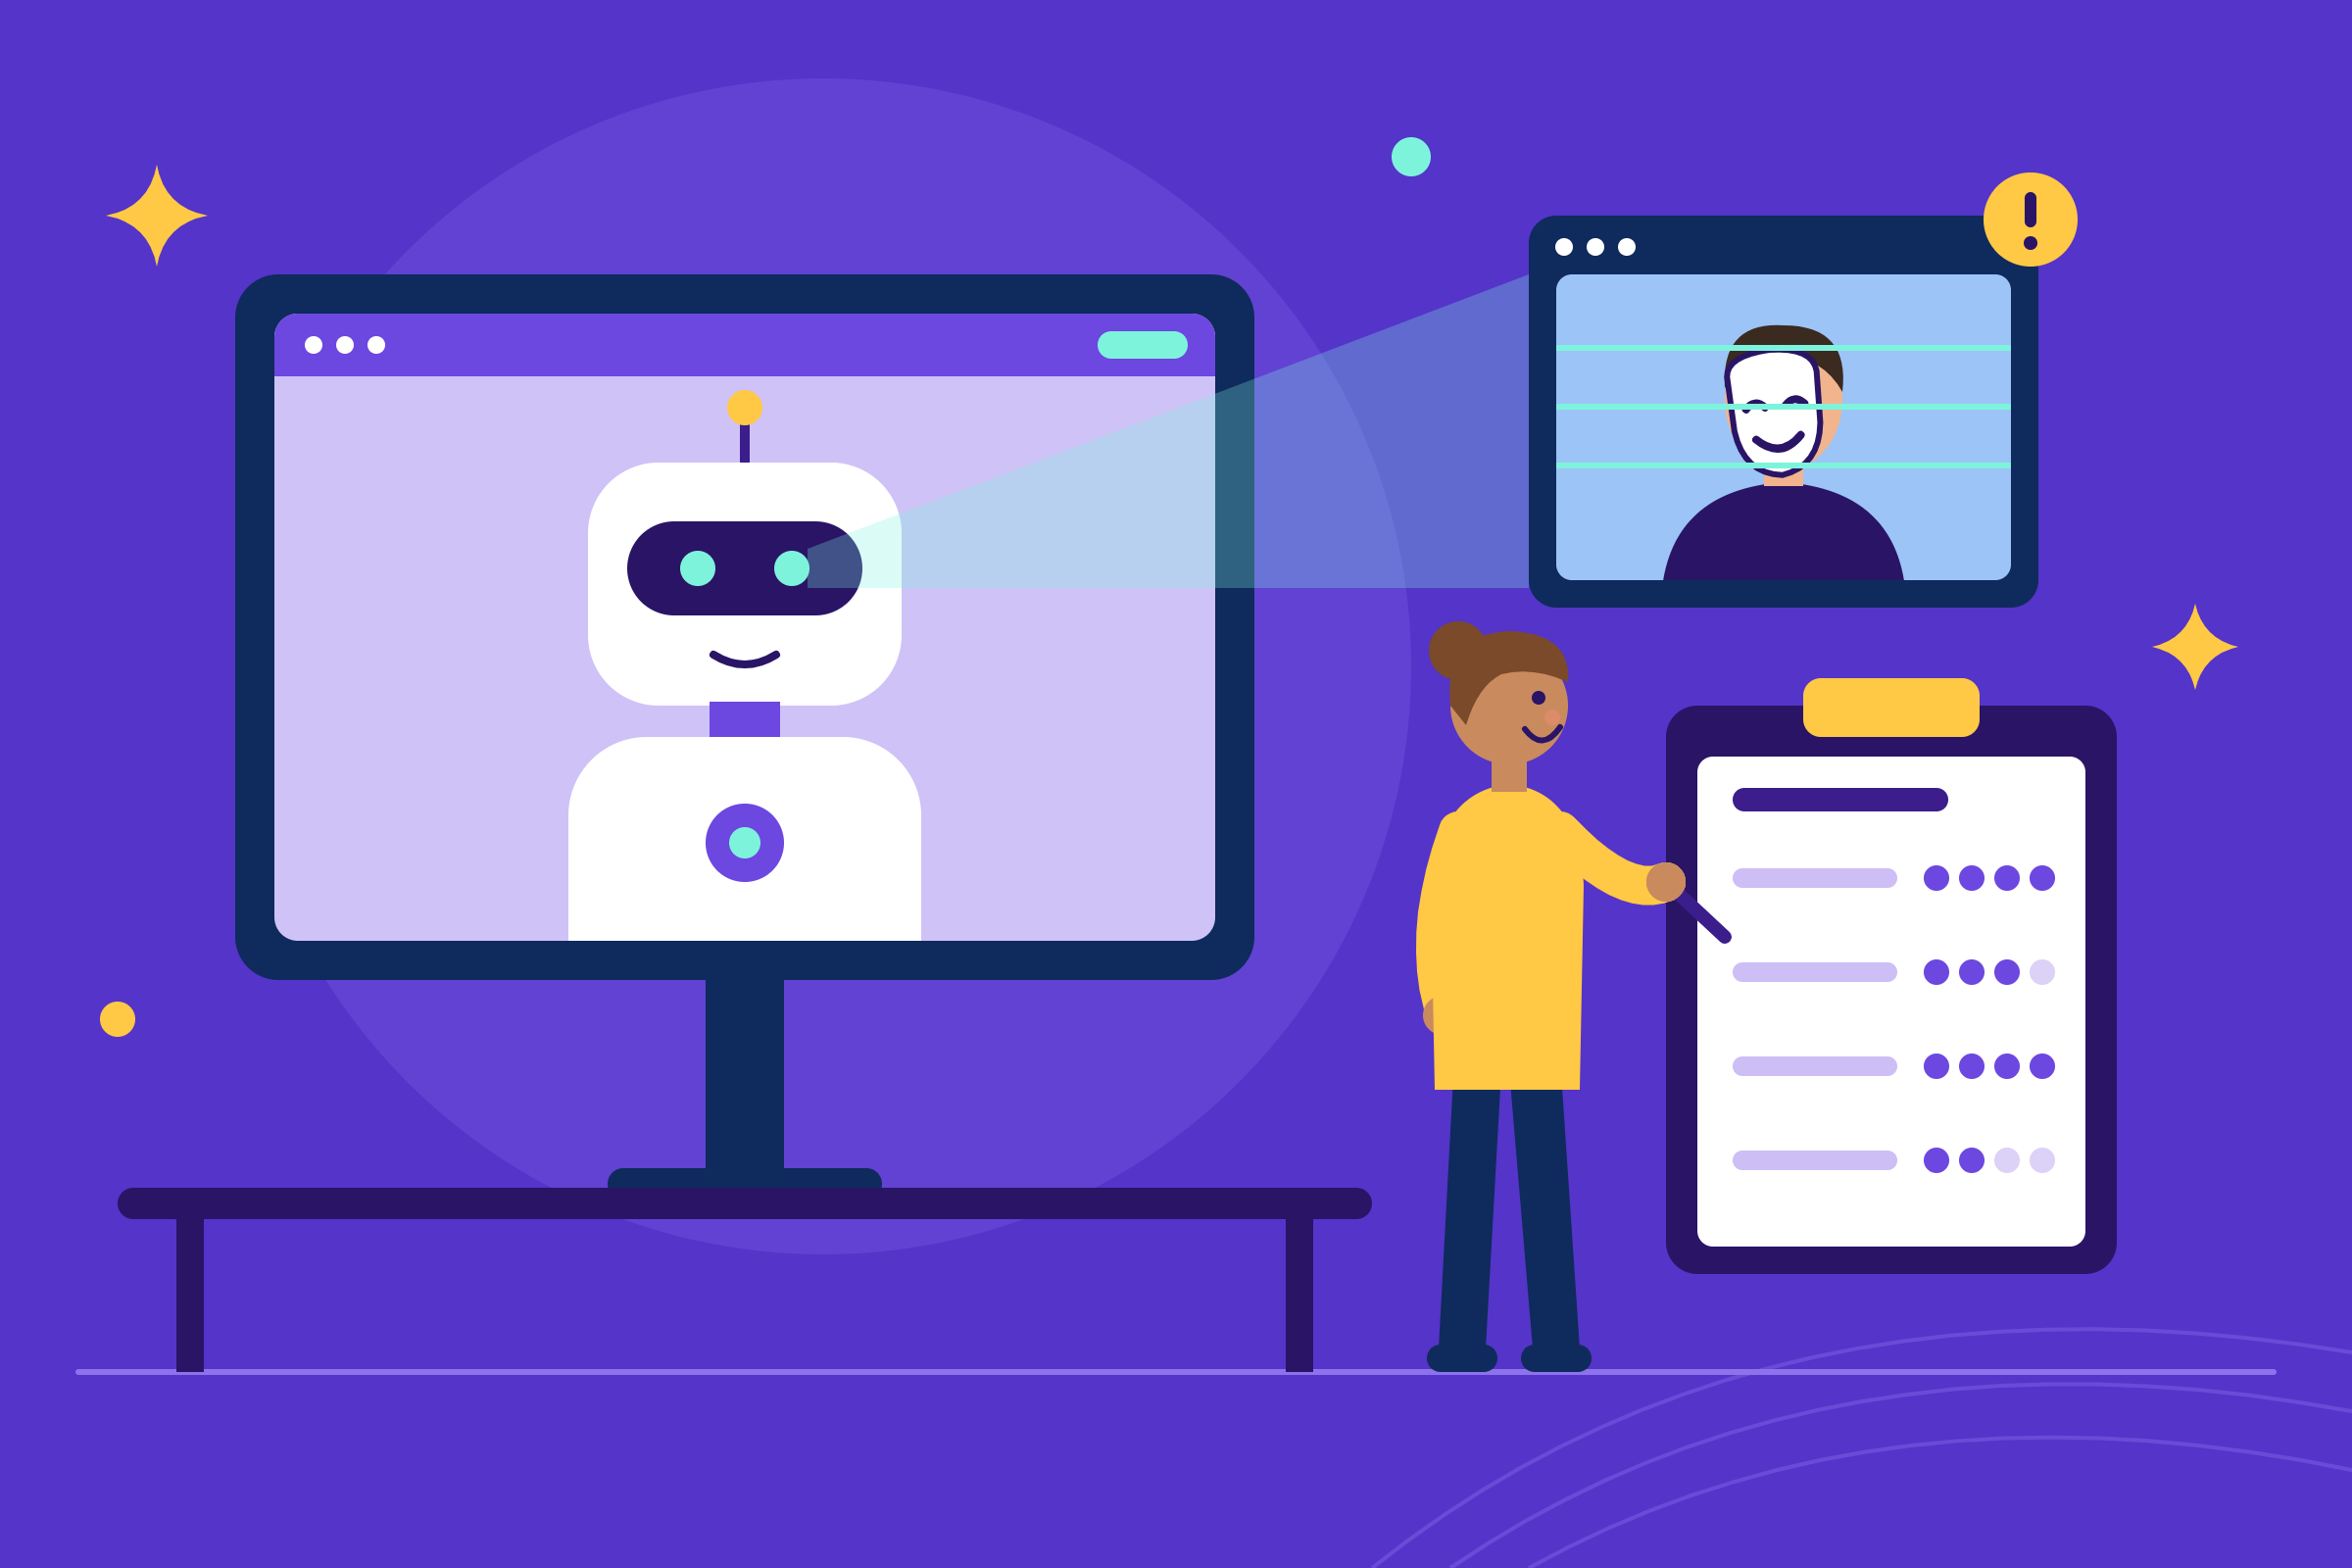
Deepfake interviews use AI-manipulated video or synthetic media to impersonate a candidate. Detection has to happen during the interview workflow, not after the fact. Our candidate fraud detection on Zoom surfaces deepfake signals natively inside the interview workflow, so your team sees risk flags when reviewing the conversation.
Detect forged candidate credentials
Credential forgery covers fake degrees, certifications, licenses, and employment verification documents. Credential verification typically splits between TA and a background check vendor, but the timing of that verification matters. Most teams verify credentials after the offer, not before the interview, and catching a forged credential after an offer has been extended is a different problem than catching it before the panel invests four hours of interview time.
Navigating the gray areas of fraud responsibility
A recruiter might spot a resume inconsistency, a hiring manager might notice a behavioral anomaly, and Security might flag a network risk signal. If each of those observations stays in its own silo, the response breaks down.
Identify fraud at every touchpoint
Map the candidate journey: application, screening interview, live interviews, offer, background check, and onboarding. Fraud enters at each touchpoint, so detection isn’t a single gate. It’s a continuous process that spans the full pipeline.
| Touchpoint | Fraud Type | Primary Detector |
|---|---|---|
| Application | Resume fraud, credential forgery | Automated fraud detection tools, Recruiter |
| Screen interview and live interviews | Imposter, deepfake, proxy interviewer, AI assistance | Recruiter, hiring manager, fraud detection tools |
| Offer and background check | Credential forgery, identity fraud | HR, background check vendor |
| Onboarding | Identity mismatch, document fraud | HR, IT, Security |
Extend fraud prevention beyond TA
Security and IT must own identity verification and technical risk, while Legal and HR must own compliance, documentation, and audit trails. The Head of TA is well-positioned to make sure each fraud type has a defined owner and that the response doesn’t stall between functions. Not because they own all of it, but because the candidate relationship and hiring workflow sit within TA’s remit.
In most cross-functional models, Security leads technical investigation and evidence collection, while Legal guides investigation procedures and HR manages employee relations and executes employment actions. Cross-functional fraud response structures that include recruiting, legal, and technology stakeholders give each fraud type a defined home and reduce the risk of signals falling between functions.
Eliminate informal handoffs from the escalation path
Without a defined escalation path, a recruiter who flags something off often has nowhere documented to send it. The concern gets passed informally to a hiring manager, nothing is written down, and Legal never sees it. Informal handoffs create liability and inconsistent responses.
Most fraudulent hires gain access to corporate credentials and systems before the discrepancy is caught, and the window between onboarding and discovery can run several days. You’re measuring the cost of an improvised response in security exposure, not just a bad hire. Without a defined escalation path, the same fraud signal gets handled differently every time it surfaces, depending on who noticed it and who they happened to call.
Mapping fraud oversight
Each function in the fraud response owns a distinct piece of the risk. Defining those pieces in advance is what separates a coordinated response from a post-incident blame conversation.
Equip recruiters to identify candidate risk
Recruiters often see the first signals: inconsistencies surfaced during resume review, screening interviews, and candidate communication. Their role is to flag concerns and escalate to the defined owner in the RACI, rather than lead the investigation themselves. We run structured async AI screening interviews with BrightHire Screen, creating a recorded first-round signal that gives recruiters documented evidence to reference when they escalate a concern.
Secure the candidate fraud workflow
Security is the natural home for identity verification, device and network risk, and deepfake signal review . These are technical investigation functions, and the expertise and tooling to handle them sits in Security in most organizations. They provide the technical tools and the investigation capability, but Security’s involvement should be defined in advance, not triggered ad hoc when a recruiter’s Slack message reaches the right person.
Our fraud detection, covering deepfake signals and session metadata, gives Security a structured signal to investigate rather than an anecdotal concern.
Ensure defensible hiring practices
Legal typically guides compliance in fraud response, covering investigation procedures, regulatory requirements, and ensuring that consent workflows, documentation standards, and audit trails meet applicable standards. HR typically manages the employee relations side of a confirmed fraud case. Coordinating with TA and Legal, and executing the resulting employment actions, which may include rescinding an offer or initiating termination.
Defensibility requires documentation at every step, and employers should retain employment records, including interview notes and recordings, for at least one year from the date of the hiring decision or from the date the record was made. Your retention policy should reflect applicable employment record requirements.
Mitigate candidate fraud at the source
Anyone on the hiring team, recruiters and hiring managers alike, is positioned to observe in-interview behavior. They may notice anomalies and inconsistencies that automated signals alone don’t fully capture, and they need training on what to look for and a clear escalation path.
Common signals worth training on include unnatural facial movements and lip-sync misalignment, as well as candidates who freeze or stall when asked to do something unscripted, a behavioral signal noted across general fraud detection guidance. Our in-interview guidance and fraud flags surface risk signals without interrupting the conversation, so hiring managers can stay focused on the candidate while the system monitors for technical anomalies.
A RACI framework for fraud accountability
Without assigned owners, every fraud incident starts with the same question: who handles this? A RACI answers that question before the incident happens. One Accountable owner per fraud type, documented in advance, so the response doesn’t stall while three functions wait for each other. RACI stands for Responsible, Accountable, Consulted, and Informed. The golden rule in RACI methodology is that only one person is Accountable per task, even when many are Responsible.
Map daily fraud responsibilities
The following table maps each fraud type to the four roles based on where detection and investigation expertise typically sits across TA, Security, Legal, and HR. These assignments are a recommended starting model, not a validated industry standard. Review them against your org structure and adjust ownership where your team’s capabilities or reporting lines differ.
| Fraud Type | Responsible | Accountable | Consulted | Informed |
|---|---|---|---|---|
| Resume fraud | Recruiter | Head of TA | Hiring manager | HR |
| Imposter candidate | Recruiter, Security | Security lead | Legal | Head of TA |
| Deepfake interview | Security, fraud detection tooling | Security lead | Head of TA | Legal |
| Forged credentials | HR, background check vendor | HR lead | Legal | Head of TA |
| Identity fraud post-hire | Security, IT | Security lead | Legal, HR | Head of TA |
Establish fraud accountability roles
Assign the Accountable role based on where the expertise sits for each fraud type. In the model above:
- Head of TA for resume fraud. It enters through the recruiting workflow.
- Security lead for imposter candidates and deepfakes. The investigation is technical.
- HR and the background check vendor for forged credentials. They hold the verification tooling and vendor relationships.
Across all fraud types, the Head of TA is well-positioned to coordinate across functions and ensure no fraud type sits without a defined owner. Standard RACI methodology applies the same single-owner logic to incident categories, which translates directly to fraud response.
Define who provides essential fraud insights
Consulted roles must be defined in advance so escalations aren’t improvised. Legal is Consulted on compliance and documentation, Security on technical risk, HR on policy, and hiring managers on in-interview observations. Standard RACI methodology warns that too many Consulted roles can lead to analysis paralysis: when every decision requires input from numerous stakeholders, the process slows to a halt. Reserve Consulted for people whose input genuinely changes the quality of the response.
Map notification flows for full visibility
Define who is Informed at each stage: detection, escalation, investigation, decision, and documentation. A simple notification flow is what keeps a contained fraud incident from becoming an organizational crisis because no one with decision authority knew it was happening. When your team detects a fraud signal, route the notification to the Accountable owner within hours, not days, and make sure TA leadership, the hiring manager, Legal, and Security each know their role in the flow before an incident occurs.
“BrightHire offers the most compelling technology I’ve ever seen for making better hiring decisions.” – Adam Grant, Advisor, Organizational Psychologist on BrightHire
Establishing your candidate fraud playbook
A RACI matrix on a slide deck isn’t an operating model. It becomes one when you map it to your actual fraud types, define escalation tiers, automate what you can, and centralize the records.
Map candidate fraud to your RACI
Start with a simple exercise: list your fraud types, assign RACI roles, and document the result. Standard RACI methodology recommends sharing the draft with everyone on it and asking two questions: “Does your column accurately reflect what you actually do?” and “Are there tasks where you should be involved but aren’t listed?” Review the RACI quarterly, not once and forget it.
Set fraud incident escalation tiers
Define escalation tiers based on severity and assign response owners and timelines for each. The tiers below are a starting template we recommend adapting to your org’s risk tolerance.
| Tier | Fraud Type | Response Owner | Timeline |
|---|---|---|---|
| Tier 1 | Resume inconsistency | Recruiter flags, TA reviews | 24 hours |
| Tier 2 | Identity mismatch | TA flags, Security investigates | 48 hours |
| Tier 3 | Confirmed fraud or deepfake | Security leads, Legal and HR involved | Same day |
Tier 3 incidents are high-impact enough that Legal and HR involvement should be coordinated as early in the response as possible. Tier 3 incidents require immediate escalation to people with the authority, expertise, and resources to act (Security, Legal, and HR) rather than waiting for the next scheduled touchpoint.
Automate candidate fraud screening
Manual fraud detection doesn’t scale. When your team runs hundreds of interviews per month, expecting recruiters and hiring managers to catch every deepfake signal and network anomaly is unrealistic. Our fraud detection runs natively during live interviews on Zoom, Microsoft Teams, and Google Meet, and through BrightHire Screen for early-round async interviews, capturing deepfake signals and session metadata and surfacing them for your team’s review as the interview happens. Signals are surfaced from each interview and available for review through the interview review workflow, and we walk through the mechanics in our webinar Inside BrightHire’s candidate fraud detection.
Centralize candidate fraud records
Fraud records have to live in the ATS, not in email threads or spreadsheets. Our ATS-synced evidence ensures that every flag, summary, and recording lives in the candidate record, so fraud signals are accessible where your team already works rather than living in a separate tool or email thread. Centralized records are what make the process defensible in an audit.
Embedding fraud detection into interview workflows
Detection works best when it’s embedded into the interview workflow itself, not bolted on as a post-call review layer. The goal is to surface risk signals without adding steps for candidates or interviewers, a theme we explored in our analysis of automated fraud tactics and our webinar on how hiring teams are responding.
Record interviews for fraud defense
Recorded interviews create the evidence base for fraud investigation, and consent workflows are a prerequisite, not an afterthought. Where GDPR applies, the lawful basis for recording candidates matters. California’s Civil Rights Council automated decision system (ADS) regulations, effective October 1, 2025, require employers to retain ADS-related hiring records for four years. A separate CPPA automated decision-making technology rule carries its own documentation requirements with a 2027 effective date for covered employers. Confirm with your legal team which obligations apply to your team’s setup.
Our compliance infrastructure includes GDPR and CCPA compliance, Zero Data Retention options, and candidate consent workflows built in by default.
Apply the RACI to fraud detection
Apply the RACI to the detection workflow itself. Who runs the tool? Who reviews flags? Who decides? Who documents? Fraud detection is a process, not a single event. Document every signal, review, and decision, giving your team a defensible trail for candidates, hiring managers, and regulators.
Clarify who flags candidate fraud during interviews
Both humans and AI flag risk, but humans make the decision. We surface deepfake and identity risk signals, the hiring team reviews them and decides, and we don’t make fraud determinations. This distinction matters for compliance: under U.S. employment law, employer liability for discriminatory hiring decisions does not transfer to the technology used to support them. Your legal team can confirm how that principle applies to your specific setup and tooling. Keeping a person in the decision loop is how you manage that responsibility. Industry analysis of deepfake hiring risks makes the same operational point: detection tooling surfaces anomalies, and trained people close the loop.
Request a demo to see how our fraud detection captures risk signals during each interview and pushes an auditable record into your ATS.
Frequently asked questions (FAQs)
The Head of TA is a natural coordinator, but the Accountable owner varies by fraud type. Security is a logical lead for identity and deepfake investigations, given where technical investigation capability typically sits. Legal is a logical lead for compliance and documentation, and HR for employment actions and policy execution.
Involve Legal and HR immediately. The offer is typically rescinded if fraud is confirmed, but the decision must be documented and consistent with company policy.
Detection should run in the background without adding steps for candidates. Our fraud detection operates during the live interview without interrupting the flow, so candidates experience a normal interview.
Yes. Hiring managers need to know what fraud signals to flag and where to escalate them. Training on emerging fraud patterns and a clear escalation path are both part of that preparation.
Quarterly, and after any fraud incident. Fraud tactics evolve, and your RACI should evolve with them.
Key Terms Glossary
Candidate fraud: Any deliberate misrepresentation by a candidate during the hiring process, including resume inflation, identity impersonation, credential forgery, or AI-manipulated video.
RACI Matrix: A responsibility assignment framework that defines who is Responsible, Accountable, Consulted, and Informed for each task or decision.
TA (Talent Acquisition): The function responsible for sourcing, screening, interviewing, and hiring candidates.
ATS (Applicant Tracking System): Software that manages the hiring workflow, candidate records, and interview scheduling.
GDPR (General Data Protection Regulation): European Union regulation governing data privacy and protection.
CCPA (California Consumer Privacy Act): California law granting consumers rights over their personal data.
SOC 2: Security and compliance framework auditing how organizations handle customer data.
Interview proxy: A person who completes an interview on behalf of the actual candidate. This is a form of imposter fraud.
Deepfake interview: An interview in which AI-manipulated video or synthetic media is used to impersonate a candidate or alter their appearance or responses.
Identity verification: The process of confirming that the person participating in the interview is the same person who applied for the role.